Data Leak Unfolds Following Ransomware Assault on Los Angeles School District
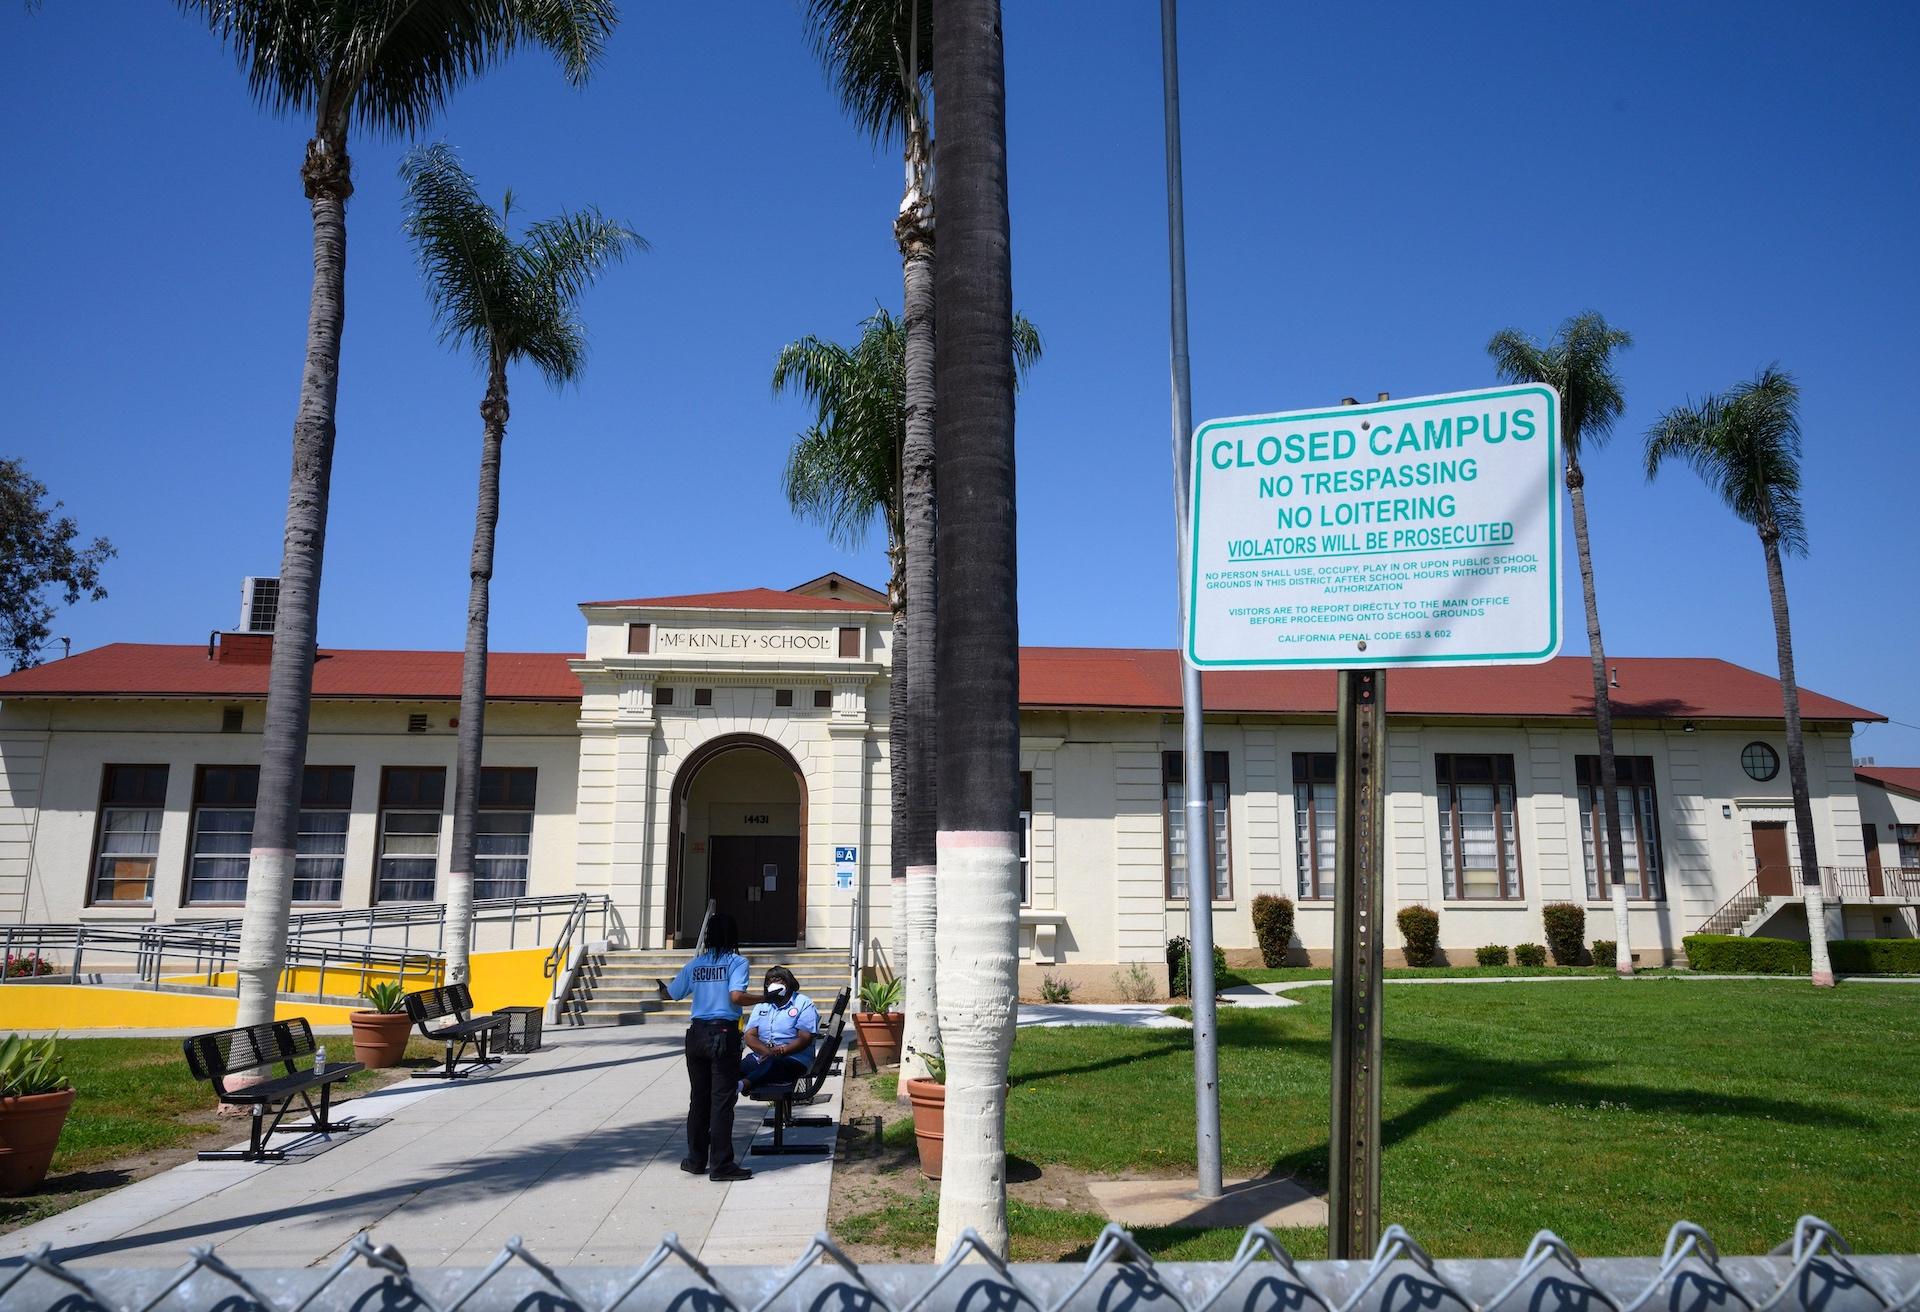
In the wake of a ransomware attack on the Los Angeles Unified School District (LAUSD), cybercriminals have begun publishing stolen confidential data, confirming their earlier threats. This breach has compromised a wide range of sensitive information, including personal details of students, educators, and administrative staff. District leadership,led by Superintendent Alberto Carvalho,has acknowledged the severity of the incident,emphasizing the increased risks of identity theft and privacy infringements for those impacted. The hackers’ decision to release fragments of the pilfered data online has escalated urgency for a rapid and effective response.
To counteract the fallout, LAUSD has implemented several immediate security initiatives designed to safeguard the community and prevent further exposure:
- Prompt alerts sent to affected parties, including advice on safeguarding personal accounts.
- Upgraded cybersecurity defenses such as enforcing multi-factor authentication and enhancing network surveillance.
- Active cooperation with law enforcement agencies to identify the perpetrators and curb additional data leaks.
| Category of Data | Degree of Exposure | Associated Threats |
|---|---|---|
| Student Information | Severe | Identity Theft, Privacy Violations |
| Employee Payroll Details | Moderate | Financial Fraud |
| Internal Messaging | Minimal | Operational Interruptions |
Dissecting the Attack Methods and Security Weaknesses Exploited in the LAUSD Breach
The cyberattack on LAUSD was orchestrated through a blend of sophisticated social engineering and exploitation of outdated technology.Initial investigations reveal that attackers employed phishing emails containing harmful links to infiltrate the district’s network. After gaining entry, they capitalized on unpatched vulnerabilities in legacy systems, which had not received timely updates, allowing them to escalate privileges and deploy ransomware across multiple servers. Notably, the absence of multi-factor authentication (MFA) on critical accounts significantly increased the risk of unauthorized access.
- Phishing attacks: Malicious payloads disguised as legitimate emails to deceive users.
- Exploitation of outdated software: Targeted vulnerabilities in email servers and legacy operating systems.
- Weak authentication protocols: Lack of MFA on administrative accounts.
- Delayed detection: Insufficient real-time monitoring allowed malware to spread undetected.
| Attack Vector | Exploited Vulnerability | Resulting Impact |
|---|---|---|
| Spear Phishing Email | Human error – credential compromise | Initial network access |
| Unpatched Software | Legacy server vulnerabilities | Privilege escalation |
| No Multi-Factor Authentication | Inadequate authentication controls | Unauthorized admin access |
Additionally, the attackers exfiltrated sensitive data prior to encrypting the systems—a tactic increasingly favored by ransomware groups to strengthen their bargaining position. Cybersecurity experts suggest the perpetrators conducted thorough reconnaissance to map the district’s network and identify critical assets, indicating a meticulously planned operation. Despite some robust defenses, LAUSD’s cybersecurity measures fell short in preventing lateral movement due to insufficient network segmentation and limited endpoint detection capabilities.
- Data theft: Extraction of valuable information before system encryption.
- Network mapping: Detailed analysis of infrastructure to target high-value systems.
- Poor network segmentation: Enabled malware to spread across multiple systems.
- Weak endpoint monitoring: Failure to detect abnormal activities early.
Privacy Consequences for Students and Staff Following Data Exposure
The ransomware incident has jeopardized the privacy of thousands within the LAUSD community, with personally identifiable information (PII) now circulating on illicit online platforms. Compromised data includes home addresses, dates of birth, social security numbers, and medical records, raising immediate concerns about identity fraud, financial scams, and unauthorized exploitation.This breach has shaken the trust of families and employees alike,highlighting the vulnerabilities educational institutions face in the digital age.
In light of these developments, the district is urging all affected individuals to remain vigilant by monitoring their financial and personal accounts closely. Free credit and identity monitoring services are being offered temporarily to mitigate potential harm. The following table summarizes the types of data exposed and their associated risks:
| Data Category | Risk Factors |
|---|---|
| Social Security Numbers | Identity theft, financial fraud |
| Academic Records | Misuse of educational information |
| Health Information | Privacy breaches, potential discrimination |
| Employee Payroll Data | Financial exploitation, phishing attempts |
Beyond the tangible risks, cybersecurity specialists warn of the psychological toll on students and staff, who may experience lasting feelings of insecurity and mistrust.The district now faces the dual imperative of bolstering its cybersecurity infrastructure while restoring confidence among its community members.
Recommendations for Educational Institutions to Fortify Cybersecurity Posture
To defend against future cyber threats, schools must adopt comprehensive cybersecurity strategies tailored to the unique challenges of educational environments. Key measures include implementing multi-factor authentication, conducting frequent vulnerability scans, and deploying advanced endpoint protection systems capable of real-time threat detection and response. Equally vital is the continuous education of staff and students on recognizing phishing attempts and social engineering tactics, fostering a culture of cybersecurity awareness and resilience. Employing data encryption and designing segmented network architectures can significantly reduce the impact of potential breaches by containing intrusions.
Investing in specialized cybersecurity personnel and forging partnerships with governmental and private cybersecurity organizations can further enhance institutional defenses. Establishing clear incident response plans and regularly conducting simulation exercises will prepare school staff to react promptly and effectively, minimizing operational disruptions and data loss. The table below highlights essential strategic actions alongside their anticipated benefits:
| Strategic Initiative | Expected Benefit |
|---|---|
| Multi-Factor Authentication (MFA) | Significantly lowers risk of unauthorized access |
| Ongoing Cybersecurity Training | Enhances awareness among staff and students |
| Network Segmentation | Restricts ransomware propagation |
| Incident Response Drills | Improves readiness and reduces response times |
Conclusion
The exposure of sensitive information following the ransomware attack on the Los Angeles Unified School District highlights the escalating dangers ransomware poses to public sector organizations. As investigations continue to unravel the full extent of the breach, this event serves as a critical reminder of the necessity for robust cybersecurity defenses and proactive vigilance in safeguarding the personal data of students and staff. Authorities remain committed to bringing the perpetrators to justice while working to prevent similar incidents in the future.